 AZ
 EN
SSH decoy
Looks like a real server. Records commands without running them.
Traps that look real. Alerts you can trust.
MVP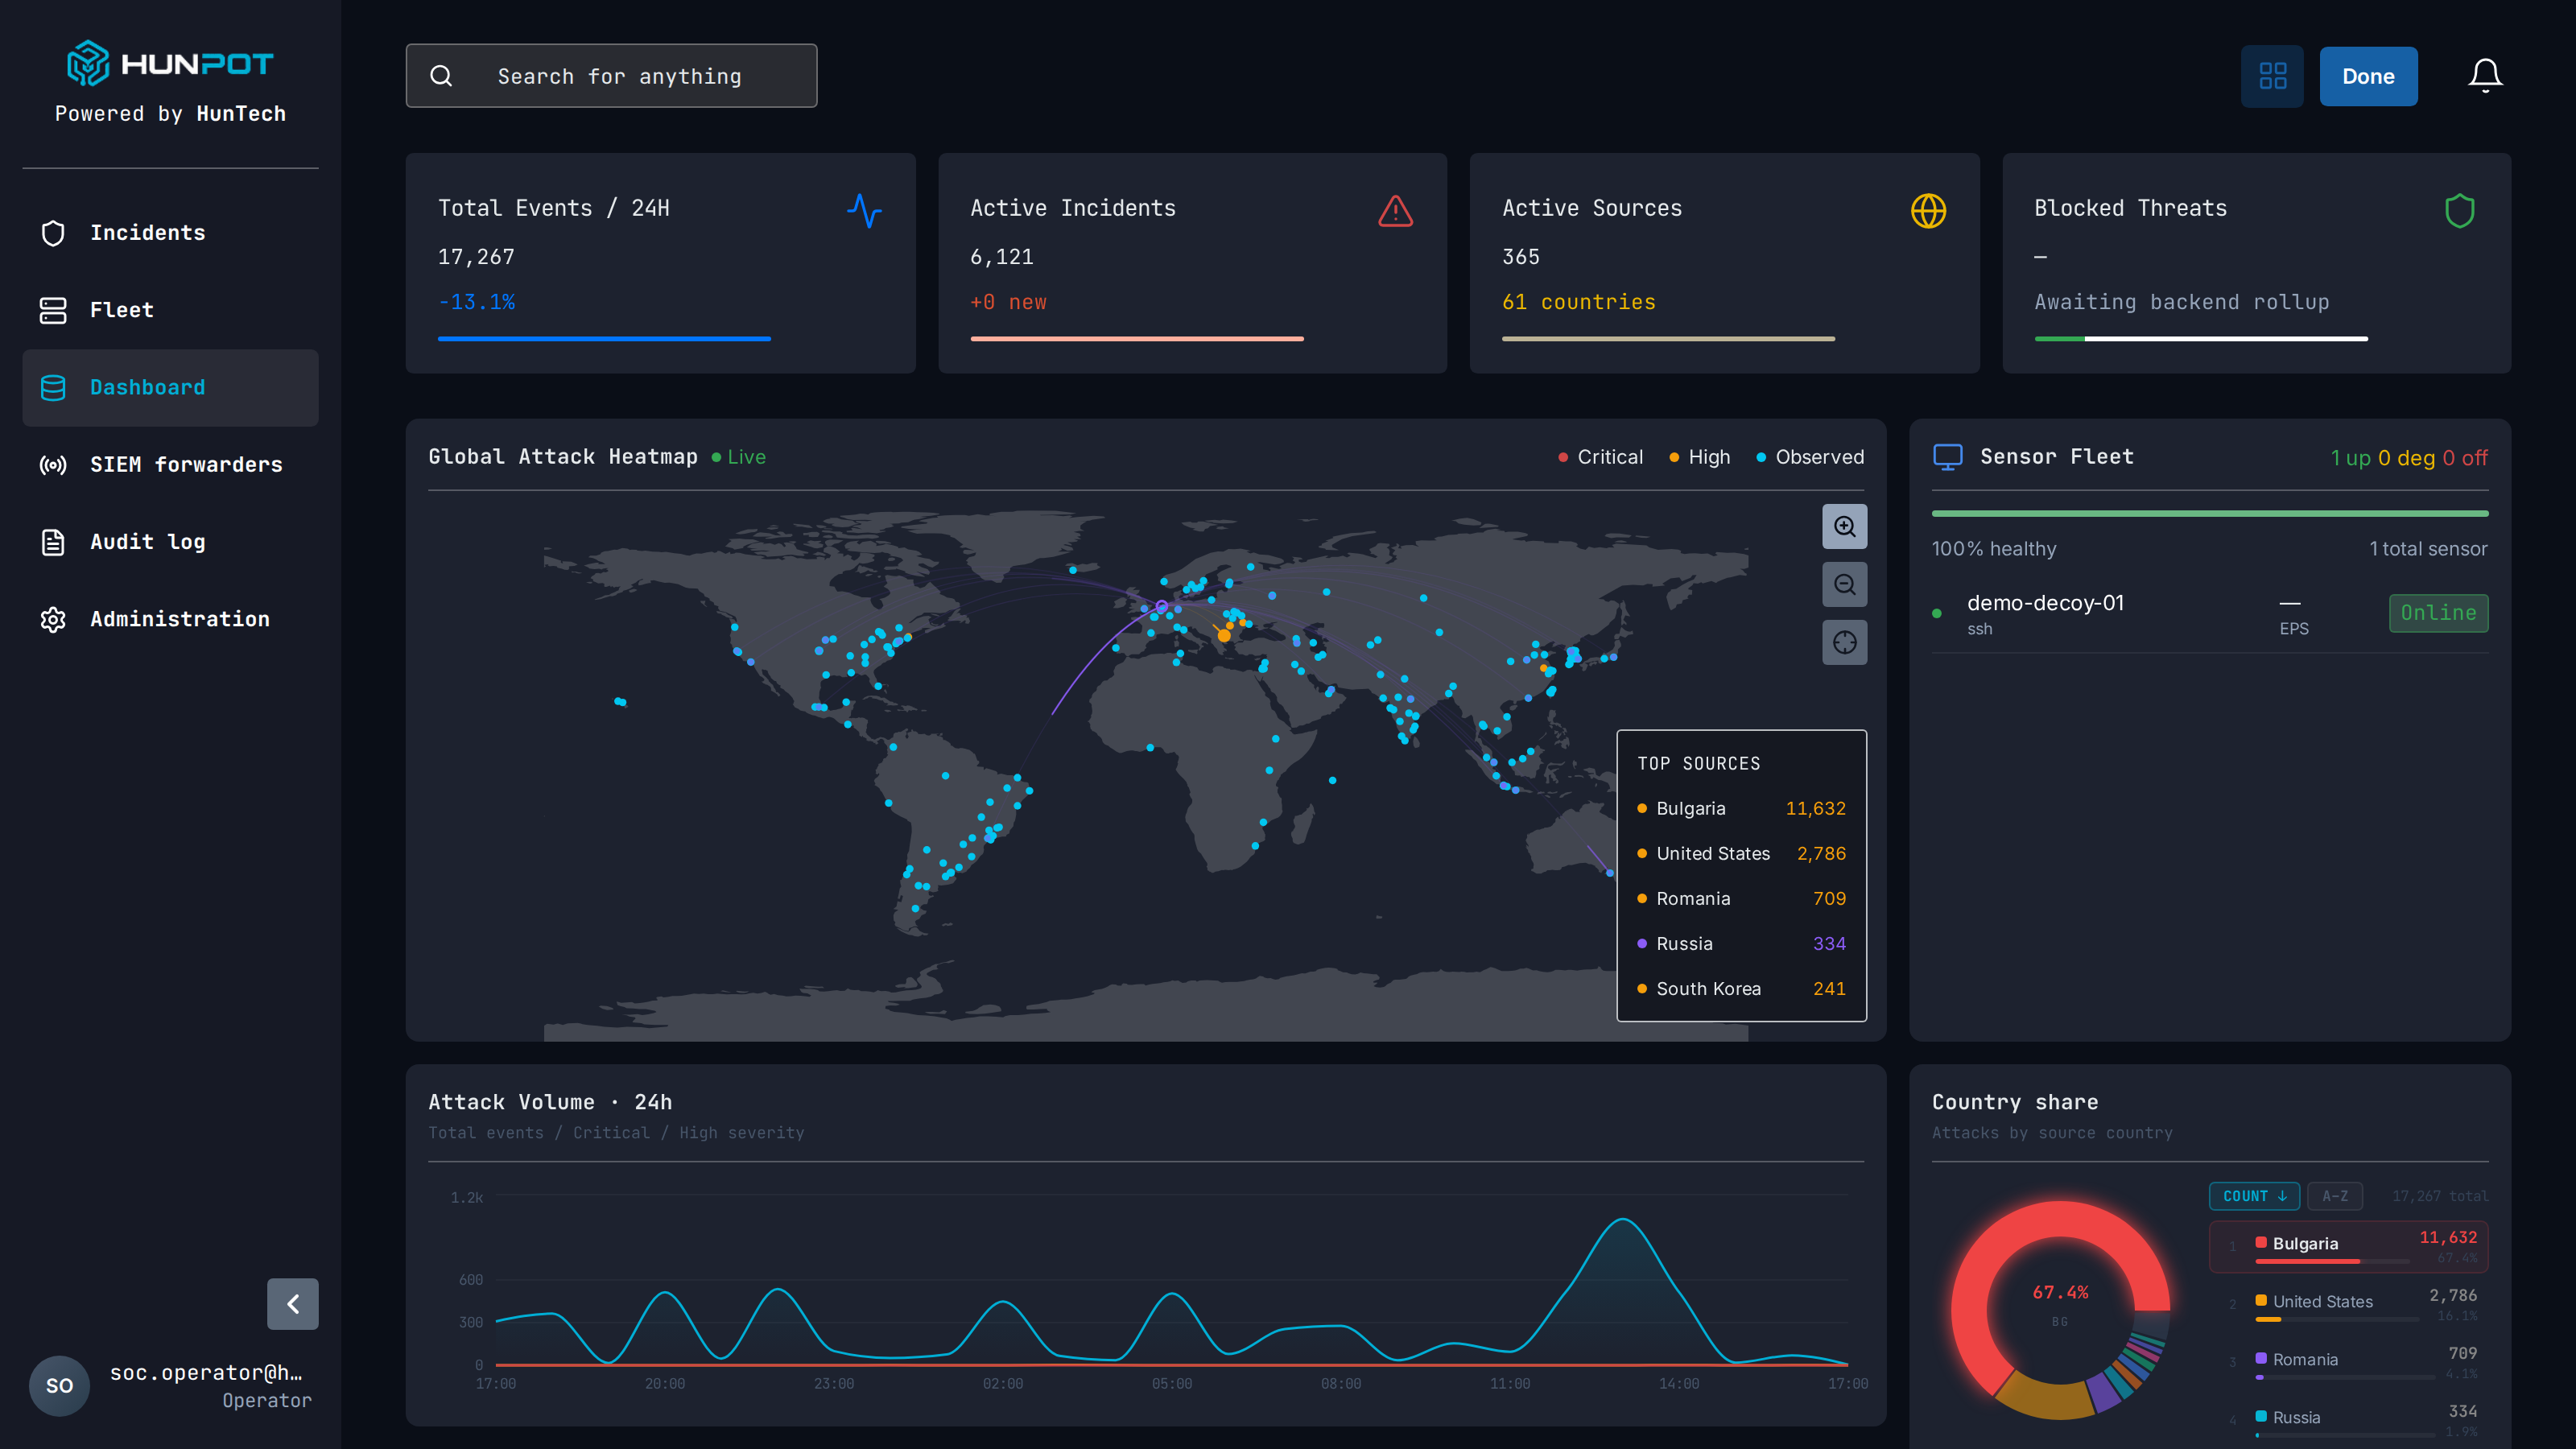
Real incidents can be buried in alert queues. HunPot records unexpected activity when an intruder interacts with a decoy.
Decoys that look like real servers record intruder activity. Legitimate users have no reason to touch them, so every interaction becomes an actionable signal.
Looks like a real server. Records commands without running them.
One incident per attack, with severity and status.
See attack sources and activity by country.
Decoy health, uptime and resource use.
Log forwarding with syslog, CEF, LEEF and JSON.
Role-based access, LDAP and an operator audit log.
Fully on-premises. The backend, console and databases run on your hardware. Data stays inside your network.
Syslog RFC 5424 · CEF · LEEF · JSON · LDAP
Banking and finance, energy and critical infrastructure, government, MSSPs and integrators.
Explore the platform with your team.